About
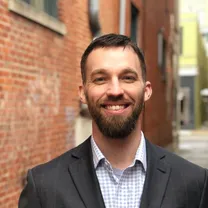
Hi, I'm Mike.
IAM Advisory Manager. I help organizations answer one deceptively simple question: who, and what, can reach your most critical systems right now?
Most access problems don't start with a breach. They start with nobody being able to answer a simple question: who, and what, can reach your most critical systems right now?
Answering that is most of my job. As an IAM Advisory Manager, I spend less time installing tools and more time helping organizations decide what they actually need, in what order, and how to prove it worked.
Where I spend my time
Zero Trust, starting with identity
Zero Trust gets sold as an architecture. In practice it's a long sequence of decisions, and most of them land on identity. I help teams pick a realistic starting point, often privileged access, and build out from there.
OT and critical infrastructure
Energy, manufacturing and healthcare, where a control-system outage is a safety event, not a ticket. The identity playbook that works in IT tends to fall apart below Purdue Level 3. I work with engineering and security teams on privileged access for vendors and engineers, non-human identities, segmentation, and programs that hold up under CAF, NIS-R and IEC 62443 scrutiny.
PKI, certificates and post-quantum readiness
Most organizations have more certificates than they can name and no plan for the day today's cryptography stops being trustworthy. I help scope the discovery, draw the line between IT PKI and OT PKI before it blurs, and turn PQC from a headline into a sequenced plan.
Two decades of building the programs
Behind the advice is twenty years of hands-on delivery: PAM with BeyondTrust, CyberArk and Delinea, access enforcement with Okta and Ping, and IGA with SailPoint wired back into PAM. I came up through the delivery side of technology, starting at Ball State University and working as a Scrum Master, Agile coach, project manager and program manager, for Fortune 500s, start-ups and plenty in between.
That mix means I can tell a board what good looks like and still hold my own in a design review.
I also hold current certifications from both CyberArk and BeyondTrustcovering privileged access, privileged remote access, endpoint privilege management, just-in-time access with Entitle, and Identity Security Insights.
Funny you should ask… exists because the same questions kept coming up in design reviews, steering committees and coffee runs. Rather than answer them one at a time, I write them up here, one question a month.
"Agile is not a process… it is a shift in mindset." Me, at the Dare to Change keynote. Security works the same way.
Certifications
Identity & security
- Privileged Remote AccessBeyondTrust · BCSE EssentialsEarned Mar 2026
- Endpoint Privilege Management for WindowsBeyondTrust · BCSE EssentialsEarned Mar 2026
- Entitle (just-in-time access)BeyondTrust · BCSE EssentialsEarned Mar 2026
- Identity Security InsightsBeyondTrust · BCSE EssentialsEarned Mar 2026
- Privileged Access ManagerCyberArk · Certified Pre-Sales Engineer (CPE)Earned Nov 2025
Delivery & leadership
- Professional Scrum Master IScrum.org · PSM IEarned May 2019
- Project Management ProfessionalProject Management Institute · PMP®Earned Aug 2010
Also:Principles of Valuation: Risk & Return, University of Michigan (2016) · Principles of Valuation: Time Value of Money, University of Michigan (2016)
Platforms I've built with
- BeyondTrustPassword Safe, EPM and remote access: mid-sized companies and one of the largest healthcare organizations
- CyberArk PAMThousands of privileged accounts across servers, databases and network devices
- CyberArk EPMRemoving local admin and enforcing least privilege on endpoints
- Delinea Secret ServerSecrets for databases, cloud and DevOps tooling
- Okta & PingAccess enforcement: SSO, MFA and adaptive policy
- SailPointIdentity governance, wired back into PAM
IndustriesEnergy · Healthcare & IoT-heavy clinical settings · Finance · Pharmacy & health insurance · Manufacturing · Consumer products · Entertainment · Professional services
Speaking
- Dare to Change — Day 2 keynoteKota Kinabalu, Sabah, Malaysia
- Digital Defense: Next Gen Cyber Minds"Secure your organization now! IAM through least privilege", virtual, Malaysia
- Stryker PMO SummitCo-presented Agile principles to nearly 200 PMs and executives
- Western Michigan UniversityGuest lecturer, IT project management, Business & Information Systems
How I review tools
Vendor reviews are only useful if you can trust them, so here are the ground rules.
- Hands-on first. I review what I've deployed, run in a lab or evaluated in a real selection, and I tell you which.
- Nobody pays to be here. Vendors can't buy a review, a rating or a spot on a list.
- Relationships are disclosed. If I hold a vendor's certification or have worked with them, the review says so up top.
- Dated and versioned. Products change fast. Every review shows what I tested and when, and I revisit them.
- Same yardstick every time. Deployment effort, day-two operations, coverage, integrations, reporting and audit, and total cost.
Let's talk
If you're working on privileged access, OT identity, or certificate and PQC readiness, I'm always up for a chat. Find me on LinkedIn. And if you have a question you'd like answered here, send it over. It might become a future post.
Opinions are my own and not those of any employer or client, past or present.